Topic 1.5 Notes – Leveraging AI in Cyber Defense
What AI in Cyber Defense Does
AI helps defenders preserve confidentiality, integrity, and availability. That means keeping data private, accurate, and usable. AI is a defensive aid, not something that gets to run security on its own.
AI can help with a few specific jobs:
- analyze security configurations such as firewall rules and access controls
- analyze application code for possible vulnerabilities
- analyze digital events from logs and systems
- suggest detection rules
- alert people or take preapproved corrective actions
The exam loves this distinction:
- AI output is a recommendation, classification, or suggestion
- a qualified human reviews important outputs before they are used
Who reviews depends on the task:
- configuration changes → security technician
- code fixes → programmer
- detection rules → detection engineer
Where AI Helps Defenders
These jobs fit into three connected parts of defense.
Prevention and protection
AI can review security configurations and look for problems like:
- overly broad permissions such as everyone being able to open payroll files
- redundant or conflicting rules that make security messy or weaker
- missing restrictions that should be there
- settings that break policy or normal practice
Example. If payroll files are open to all employees, AI might recommend limiting access to HR only. A technician still has to check that change, because the wrong fix could break a real business task.
AI can also analyze application code. If code directly combines user input into a database query, AI may flag it as risky and suggest a safer method. The programmer must verify that the vulnerability is real, the fix works, and the fix does not create new bugs.
Detection
AI can suggest detection rules for security systems. A rule might look for:
- repeated failed logins
- unusual access patterns
- suspicious sequences of events
A detection engineer checks whether the rule matches the data the system actually has, whether it is too broad or too narrow, and whether normal user behavior would trigger it.
Response
After suspicious activity is found, AI can either:
- send an alert to people
- take an approved corrective action
That leads right into how AI handles huge amounts of event data.
How AI Finds Likely Threats in Massive Event Data
Networks, devices, apps, and data systems create millions of events. An event is just a recorded action, like a login attempt or file access. Humans cannot inspect all of them one by one.
AI can sort events into:
- likely malicious
- likely harmless
It may look for:
- known bad patterns
- behavior that breaks from normal activity
- ordinary events that become suspicious when seen as a sequence
- activity across multiple accounts, devices, or services
- unusual timing, frequency, source, or context
In practice, that classification step is part of a larger workflow where AI helps sift inputs, then people review what the system suggests before any action is taken.
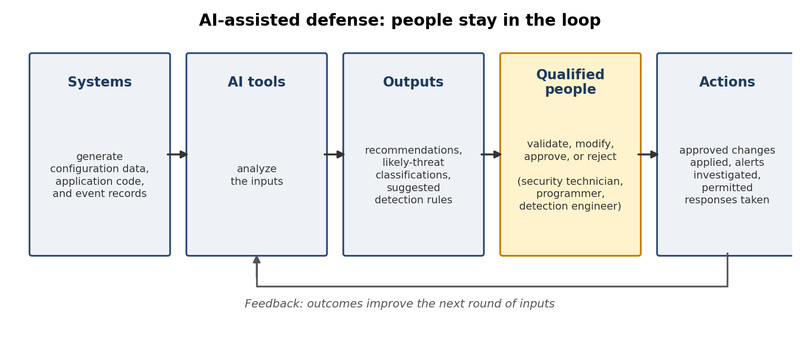
AI-assisted cybersecurity workflow
This is prioritization, not proof. Likely malicious does not mean confirmed malicious.
Two terms to know cold:
- false positive = harmless activity flagged as malicious
- false negative = real malicious activity missed
Alerts, Corrective Actions, and Why Human Review Matters
An alert asks a person to investigate. A corrective action changes the system.
Corrective actions can include:
- blocking traffic
- disabling or limiting an account
- isolating a device
- stopping a process
The safest automated actions are usually high-confidence, limited, and reversible. Over-automation can lock out real users or disrupt business. Human review matters because AI can be wrong, incomplete, or missing organization-specific context.
The Full AI-Assisted Defense Workflow
Here is the full picture in one example. AI notices payroll-folder access is too broad, flags unsafe filename-handling code, and detects unusual payroll downloads from one account. Then humans review the access fix, the code fix, and the suspicious activity. The system may temporarily stop the session if that response was approved ahead of time.
AI gives defenders speed and scale. Humans provide judgment, context, and responsibility.
Key Takeaways
AI-Powered Cybersecurity Tool
A tool that analyzes security data at machine scale to recommend protections, identify likely threats, generate alerts, or perform authorized responses while qualified humans retain oversight
Security Configuration
The settings and rules that determine how a system applies security controls, such as firewall rules and access controls
AI Security-Configuration Review
AI examination of current security settings to find excessive, conflicting, missing, or policy-inconsistent controls and recommend safer options for a security technician to review
AI Application-Code Analysis
AI inspection of application code to flag possible vulnerabilities and recommend mitigations that a knowledgeable programmer must verify and test
Automated Detection System
A system that uses rules or other analytic methods to identify events and patterns that may indicate an attack
Detection Rule
Conditions an automated detection system treats as suspicious and the action it takes when they occur; AI-suggested rules require review by a detection engineer
Digital Event
A recorded occurrence in a digital system, such as an authentication attempt, connection, application request, file change, or process execution
AI-Powered Digital-Event Analysis
Machine-scale analysis that sorts and prioritizes digital events by how likely they are to represent malicious activity rather than harmless activity
False Positive vs. False Negative
A false positive labels harmless activity as malicious; a false negative fails to identify actual malicious activity
Alert vs. Corrective Action
An alert requests human attention and investigation; a corrective action changes a system's state to contain or stop suspected malicious activity
Automated Response
A corrective action automatically performed after detection when the organization has authorized that action in advance
Notes
AI-Powered Cybersecurity Tool
A tool that analyzes security data at machine scale to recommend protections, identify likely threats, generate alerts, or perform authorized responses while qualified humans retain oversight
Security Configuration
The settings and rules that determine how a system applies security controls, such as firewall rules and access controls
AI Security-Configuration Review
AI examination of current security settings to find excessive, conflicting, missing, or policy-inconsistent controls and recommend safer options for a security technician to review
AI Application-Code Analysis
AI inspection of application code to flag possible vulnerabilities and recommend mitigations that a knowledgeable programmer must verify and test
Automated Detection System
A system that uses rules or other analytic methods to identify events and patterns that may indicate an attack
Detection Rule
Conditions an automated detection system treats as suspicious and the action it takes when they occur; AI-suggested rules require review by a detection engineer
Digital Event
A recorded occurrence in a digital system, such as an authentication attempt, connection, application request, file change, or process execution
AI-Powered Digital-Event Analysis
Machine-scale analysis that sorts and prioritizes digital events by how likely they are to represent malicious activity rather than harmless activity
False Positive vs. False Negative
A false positive labels harmless activity as malicious; a false negative fails to identify actual malicious activity
Alert vs. Corrective Action
An alert requests human attention and investigation; a corrective action changes a system's state to contain or stop suspected malicious activity
Automated Response
A corrective action automatically performed after detection when the organization has authorized that action in advance
