Topic 2.3 Notes – Protecting Physical Spaces
What Protecting Physical Spaces Means
If someone can physically reach a device, room, or building, they may get around software defenses fast. A thief can steal a laptop, plug malware into a USB port, read papers on a desk, or shut systems down by cutting power.
This topic is about layered, risk-based protection. That means:
- Find the physical weakness
- Think about how an attacker would use it
- Pick controls that reduce that risk
You’ll see three control functions across this topic:
- Preventive controls block or reduce the chance of an attack
- Detective controls create evidence or alerts
- Corrective controls reduce harm after something goes wrong
The Main Physical Security Controls
There are two big groups here. Managerial controls shape employee behavior through rules and training. Physical and related technical controls block access, protect devices, and keep systems running.
Keep the defense-in-depth idea in mind here. Physical security is the outer layer, but it still supports the inner layers that protect systems and data.
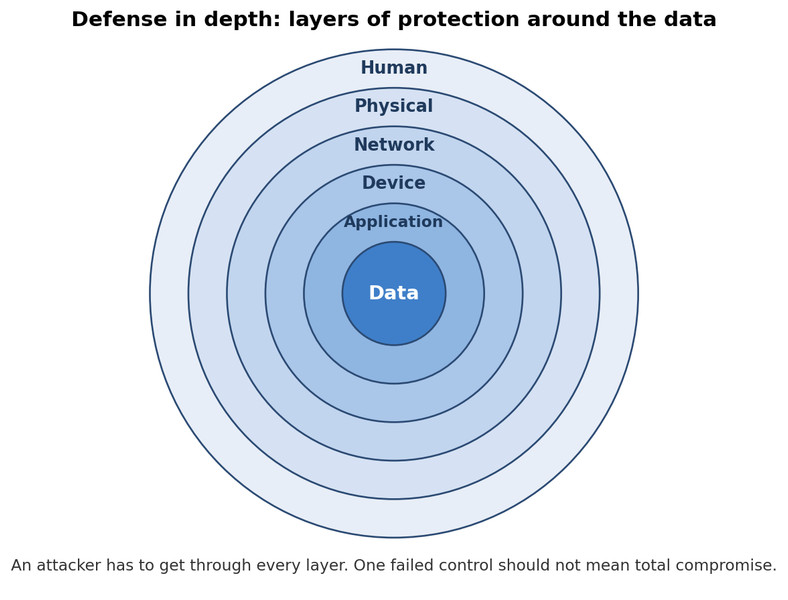
Defense in depth layers
Managerial controls
Two managerial controls matter most in this topic.
Security awareness training
Training helps employees protect physical spaces through everyday choices.
It should teach people to:
- Spot social engineering, including phishing and in-person deception like “I forgot my badge”
- Avoid letting other people into restricted areas with their own badge
- Help prevent device theft by keeping laptops and other portable devices under control
A common test trap is thinking training solves the whole problem. It doesn’t. Training helps, but people still make mistakes, so physical barriers matter too.
Workstation security policy
A workstation security policy explains how to protect devices, documents, and information where work happens. Some organizations use tiers, so systems handling sensitive data get stronger rules.
Common rules include:
- Lock unattended devices so nobody can use your signed-in session
- Clean desk policy so sensitive papers are removed or secured
- Privacy screens or barriers to reduce shoulder surfing
- Surge protectors or UPS devices to protect equipment and availability
One distinction you need clear in your head: a session lock protects a logged-in account, and a physical computer lock helps stop theft. Those are different controls.
Physical and related technical controls
These controls protect the building, the room, the device, or the power supply.
- Fences, gates, bollards deter and restrict approach to a building
- Bollards are especially about limiting vehicle access
- Locks protect doors, server cabinets, and computers from theft or unauthorized access
- Card readers deny unauthorized badges and record which badge was used and when
- Access control vestibules and turnstiles help limit entry to one person per authorization
- Disable USB ports to stop malware-loaded drives or malicious peripherals
- UPS and generators keep power available during outages
- UPS = short-term backup for a device
- Generator = larger-scale, longer backup
A secured entry vestibule is a good example of a control that works with badges or other access checks to reduce tailgating.
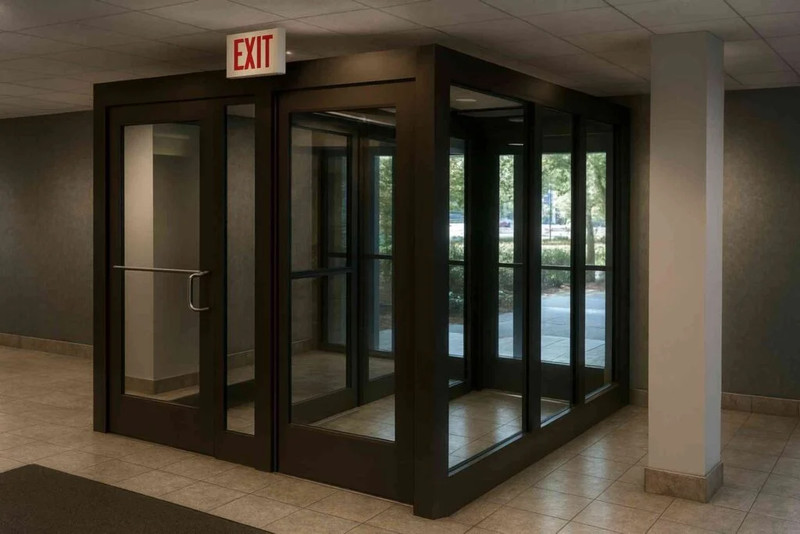
Access control vestibule
How These Controls Match Specific Risks
This part gets tested a lot in scenarios. The question usually gives you a vulnerability and asks for the best mitigation.
Use this chain:
- Identify the asset and the physical vulnerability
- Explain how an attacker could exploit it
- State the effect on confidentiality, integrity, or availability
- Choose a control that prevents, detects, or corrects it
- Explain why that control fits
- Decide whether another layer is needed
Common matches:
- Unlocked building approach → fencing, gates, bollards
- Unlocked room or cabinet → locks
- Need to restrict badge access and keep entry records → card readers
- One valid badge could let in several people → vestibules or turnstiles
- Signed-in device left alone → session lock
- Sensitive papers left out → clean desk policy
- Screen visible to others → privacy screen
- Open USB access → disable ports
- Short outage → UPS
- Long outage affecting larger systems → generator
Important wording:
- Piggybacking means an authorized person is talked or tricked into letting someone in
- Tailgating means someone follows in without being noticed
- Card reader logs the badge used, not guaranteed true identity if the badge was stolen or cloned
Why Layering and Prioritizing Matter
No single control covers every risk. A lock won’t help during a blackout. A UPS won’t stop theft. A card reader alone won’t stop someone slipping in behind an employee.
That’s defense in depth. You stack controls so one weakness doesn’t expose everything.
Mitigations are prioritized by:
- Risk severity
- How much damage would happen? Think stolen data, downtime, lost devices, interrupted service.
- Cost
- Purchase, setup, maintenance, staffing, training, inconvenience
For a server in an unlocked room with exposed USB ports and frequent outages, strong choices would be room locks, cabinet locks, disabled USB ports, and a UPS. A card reader adds access control and logs. A vestibule only makes sense if tailgating risk is high enough. A generator is worth it if long downtime would hurt badly.
Key Takeaways
Security Awareness Training
A managerial control that teaches employees to detect social engineering, avoid admitting others with their badges, and help prevent device theft
Social Engineering
Psychological manipulation that induces a target to take an action benefiting an adversary
Workstation Security Policy
A managerial control specifying required protections for workplace devices, documents, and information, sometimes with stronger tiers for sensitive data
Session Lock
A lock on an active user session that prevents others from using an unattended, already-authenticated device
Clean Desk Policy
A requirement to remove or secure sensitive papers and exposed information when a workstation is unattended
Privacy Screen Filter
A physical screen barrier that limits viewing from outside the intended position and mitigates shoulder surfing
Surge Protector
A device that protects equipment from damaging voltage spikes but normally does not provide backup power
Uninterruptible Power Supply (UPS)
A limited backup power source that keeps devices operating briefly or allows an orderly shutdown when normal power fails
Fencing
A physical barrier that defines a controlled perimeter and deters or restricts pedestrian approaches
Gate
A controlled passage point through a physical perimeter
Bollard
A sturdy post that restricts vehicles from approaching entrances, equipment, or other protected areas
Physical Lock
A restraint on a door, cabinet, or computer that helps prevent unauthorized entry, theft, or hardware access
Card Reader
An entry control that denies unauthorized badges and records which credential was used at a location and time
Piggybacking vs. Tailgating
Piggybacking is knowingly admitting an unauthorized person; tailgating is an unauthorized person following without the authorized person’s awareness
Access Control Vestibule
A controlled two-door passage in which the first door generally closes before the second opens, limiting entry on one authorization
Turnstile
A physical entrance control that limits how many people can pass for each authorization
Disabling USB Ports
Blocking or limiting USB device access to prevent external drives or malicious peripherals from compromising a computer
Generator
A larger-scale backup power source that can support a building or critical systems during an extended outage
Selecting a Relevant Mitigation
Identify the asset and vulnerability, trace its exploitation and CIA impact, choose a control that changes the attack, and evaluate remaining risk
Mitigation Prioritization
Ranking relevant controls by risk severity and total cost so resources address the most consequential risks cost effectively
Defense in Depth
Using multiple complementary security layers so different attack paths are addressed and one control’s failure does not expose the asset
Notes
Security Awareness Training
A managerial control that teaches employees to detect social engineering, avoid admitting others with their badges, and help prevent device theft
Social Engineering
Psychological manipulation that induces a target to take an action benefiting an adversary
Workstation Security Policy
A managerial control specifying required protections for workplace devices, documents, and information, sometimes with stronger tiers for sensitive data
Session Lock
A lock on an active user session that prevents others from using an unattended, already-authenticated device
Clean Desk Policy
A requirement to remove or secure sensitive papers and exposed information when a workstation is unattended
Privacy Screen Filter
A physical screen barrier that limits viewing from outside the intended position and mitigates shoulder surfing
Surge Protector
A device that protects equipment from damaging voltage spikes but normally does not provide backup power
Uninterruptible Power Supply (UPS)
A limited backup power source that keeps devices operating briefly or allows an orderly shutdown when normal power fails
Fencing
A physical barrier that defines a controlled perimeter and deters or restricts pedestrian approaches
Gate
A controlled passage point through a physical perimeter
Bollard
A sturdy post that restricts vehicles from approaching entrances, equipment, or other protected areas
Physical Lock
A restraint on a door, cabinet, or computer that helps prevent unauthorized entry, theft, or hardware access
Card Reader
An entry control that denies unauthorized badges and records which credential was used at a location and time
Piggybacking vs. Tailgating
Piggybacking is knowingly admitting an unauthorized person; tailgating is an unauthorized person following without the authorized person’s awareness
Access Control Vestibule
A controlled two-door passage in which the first door generally closes before the second opens, limiting entry on one authorization
Turnstile
A physical entrance control that limits how many people can pass for each authorization
Disabling USB Ports
Blocking or limiting USB device access to prevent external drives or malicious peripherals from compromising a computer
Generator
A larger-scale backup power source that can support a building or critical systems during an extended outage
Selecting a Relevant Mitigation
Identify the asset and vulnerability, trace its exploitation and CIA impact, choose a control that changes the attack, and evaluate remaining risk
Mitigation Prioritization
Ranking relevant controls by risk severity and total cost so resources address the most consequential risks cost effectively
Defense in Depth
Using multiple complementary security layers so different attack paths are addressed and one control’s failure does not expose the asset
