Topic 4.3 Notes – Protecting Devices
What Protecting a Device Means
A host is one device on a network. Protecting a device means lowering the chance that that one machine gets infected, exploited, or used by an attacker.
The three control groups here work as defense in depth. They cover different risks:
- Managerial controls tell users what they may, must, or must not do.
- Anti-malware and updates deal with malicious files and known software flaws.
- Host-based firewalls control network traffic to and from one device.
The image shows defense in depth as layered protection. For this section, focus on the layers that apply directly to a single device, especially host controls.
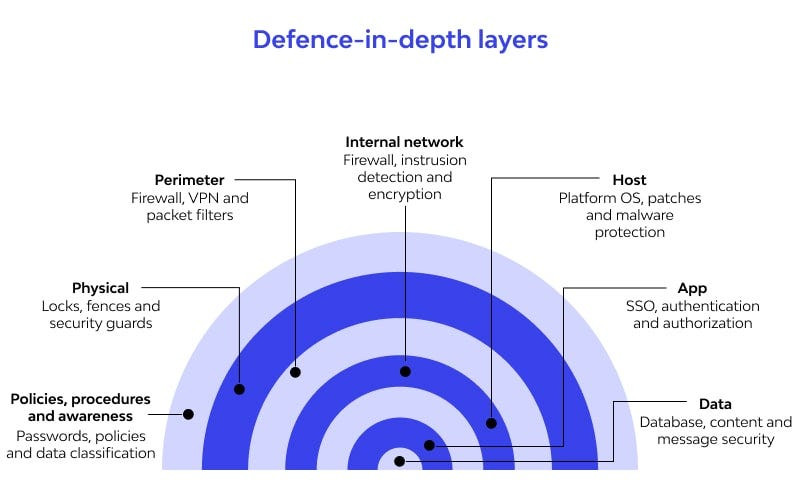
Defense-in-depth layers
No single layer is enough.
- A policy only helps if users follow it or the system enforces it.
- Anti-malware mainly catches known malware.
- Updates fix known vulnerabilities.
- A firewall only blocks traffic that its rules actually deny.
Managerial Controls for Device Security
A policy sets the rule. The device may have settings that enforce that rule, but the policy itself is the managerial control.
Acceptable use policy
An acceptable use policy explains how organization-owned devices may be used.
Common rules include:
- banning certain sites, such as social media or gaming
- requiring software to stay updated
- allowing or limiting peripherals like printers, cameras, or phones
- blocking external drives or removable media like USB storage
This matters because users often create risk by what they click, install, or plug in. An AUP cuts down chances for malware infection and data being copied to removable media.
Password policy
A password policy sets the organization’s password requirements.
It may include:
- minimum or maximum length
- how long a password can be kept
- no reuse of old passwords
- construction rules, like no dictionary words or required character types
- using a password manager instead of writing passwords down
On tests, watch the wording. If the rule is about what passwords must be like, that is password policy.
Software installation policy
A software installation policy controls what software users can install.
It often includes:
- users cannot install software on their own
- an approved software list
- a request process for special software needed for a job
This reduces risk from malware, fake apps, unsupported software, and outdated software.
Anti-Malware and Software Updates
These are technical controls. They act directly on the device.
How anti-malware works
A signature is a detectable pattern tied to known malware.
The process is:
- Anti-malware scans files.
- It compares them to a signature database.
- If a file matches, it is quarantined.
- Then it is removed or neutralized.
This flow is what that decision looks like in practice.
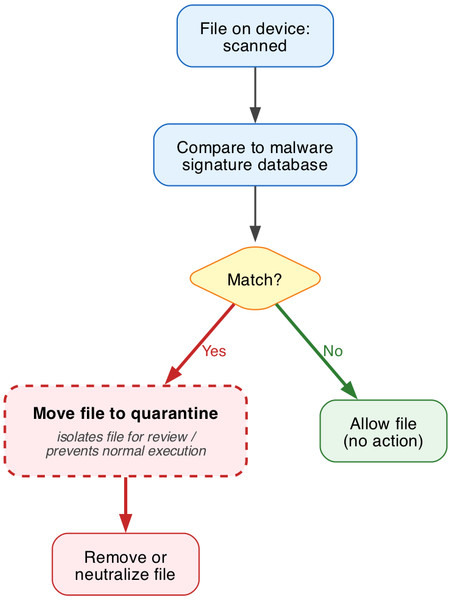
Anti-malware signature matching and quarantine
Quarantine matters because it isolates the suspicious file first. That keeps it from running normally and gives time for review.
The big limit is that new or changed malware may not match a known signature.
Why updates and patches matter
A vulnerability is a weakness in software. A vendor fixes it by releasing an update. A small update is a patch.
The sequence is simple:
- A vulnerability is found.
- A fix is created.
- An update is released.
- The device installs it.
- The known attack path is closed.
Both the operating system and applications must be updated. An unpatched browser can still be exploited even if the OS is current.
Host-Based Firewalls
A host-based firewall is software that protects one device. It filters both inbound traffic coming in and outbound traffic leaving the device.
That matters because even on a bad network, the device still has its own traffic filter.
What rules can match
Firewall rules can allow or deny traffic based on:
- direction
- source IP
- destination IP
- source port
- destination port
- service
- protocol
- application
Rule order and first match
A firewall uses an ordered ACL. The first matching rule applies.
This is a classic exam trap. If a broad allow rule comes before a specific deny rule, the deny may never happen.
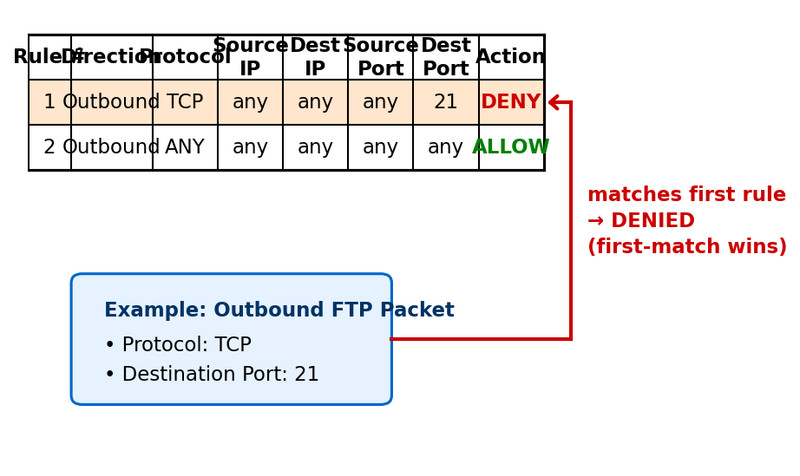
First-match firewall rule example
Worked example: blocking outbound FTP
To block a host from sending FTP traffic out, the rule should be:
- Direction outbound
- Protocol TCP
- Destination port 21
- Action deny
The easy mistake is choosing source port 21. For normal outbound client traffic, you usually match the destination port because the remote server is listening on that port.
Key Takeaways
Managerial Controls
Organizational rules, policies, and procedures that govern user behavior and security practices rather than directly filtering traffic or scanning files
Acceptable Use Policy (AUP)
A policy defining permissible, prohibited, and required uses of organization-owned devices
Password Policy
A policy defining requirements for creating, using, changing, and managing organizational passwords
Software Installation Policy
A policy defining what software users may install, which applications are approved, and how users request additional software
Anti-Malware Software (Antivirus Software)
Software that scans files for known malware signatures and quarantines and removes matching malicious files
Malware Signature
A detectable characteristic pattern associated with a known malicious file or piece of code
Quarantine
Isolation of a suspected malicious file so it cannot operate normally or affect the rest of the system
Software Update
A vendor-distributed software fix that closes known vulnerabilities; operating systems and applications must both be kept current
Patch
A small software update, often distributed to correct a known vulnerability
Host-Based Firewall
Software on one device that allows or denies its inbound and outbound network traffic according to firewall rules
Access Control List (ACL)
An ordered set of firewall rules specifying which traffic to allow or deny
Inbound vs. Outbound Traffic
Inbound traffic arrives at the protected device; outbound traffic leaves the protected device
Ordered Firewall Rule Processing
Evaluate rules from first to last, apply the first matching rule, and ignore all later rules
Host-Based Firewall Rule Criteria
Direction, source or destination IP address or port, service, protocol, or application used to decide whether to allow or deny traffic
Notes
Managerial Controls
Organizational rules, policies, and procedures that govern user behavior and security practices rather than directly filtering traffic or scanning files
Acceptable Use Policy (AUP)
A policy defining permissible, prohibited, and required uses of organization-owned devices
Password Policy
A policy defining requirements for creating, using, changing, and managing organizational passwords
Software Installation Policy
A policy defining what software users may install, which applications are approved, and how users request additional software
Anti-Malware Software (Antivirus Software)
Software that scans files for known malware signatures and quarantines and removes matching malicious files
Malware Signature
A detectable characteristic pattern associated with a known malicious file or piece of code
Quarantine
Isolation of a suspected malicious file so it cannot operate normally or affect the rest of the system
Software Update
A vendor-distributed software fix that closes known vulnerabilities; operating systems and applications must both be kept current
Patch
A small software update, often distributed to correct a known vulnerability
Host-Based Firewall
Software on one device that allows or denies its inbound and outbound network traffic according to firewall rules
Access Control List (ACL)
An ordered set of firewall rules specifying which traffic to allow or deny
Inbound vs. Outbound Traffic
Inbound traffic arrives at the protected device; outbound traffic leaves the protected device
Ordered Firewall Rule Processing
Evaluate rules from first to last, apply the first matching rule, and ignore all later rules
Host-Based Firewall Rule Criteria
Direction, source or destination IP address or port, service, protocol, or application used to decide whether to allow or deny traffic
