Topic 4.2 Notes – Authentication
What Authentication Is
Authentication proves identity. Authorization decides what that identity can access or do. That difference matters because a stolen password can let an attacker be treated as the real user, with that user’s permissions.
The proof used for login is an authentication factor. In this topic, secure authentication depends on three linked protections:
- Safe password storage so a stolen database does not reveal plaintext passwords
- Resistance to password attacks such as guessing, reuse, and cracking
- Strong login requirements so one stolen secret is less likely to be enough
If the compromised account is an admin account, the damage is much worse because the attacker gets higher privileges.
How Password Hashing Works
A cryptographic hash function takes input of any length and produces a fixed-length output. That output can be called a hash, checksum, message digest, or digest.
This basic idea is what the diagram is showing.
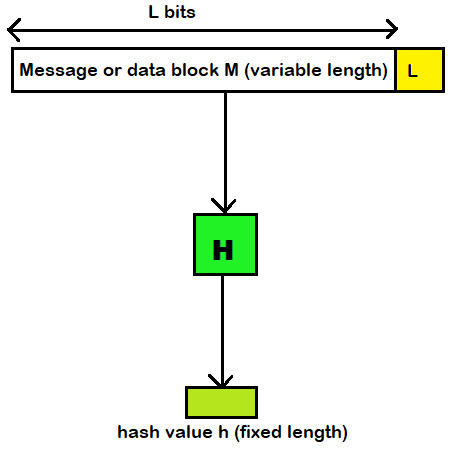
Hash function input and fixed-length output
Common names you should recognize:
- MD5
- SHA-1
- SHA-256
- SHA-512
- NTHash
- RIPEMD-160
Properties
- Collision resistance means it is hard to find two different inputs with the same output. Collisions must exist because an -bit hash has only possible outputs.
- Pre-image resistance means that given a hash, it is infeasible to recover the original input.
- Repeatability means the same input always gives the same hash.
- Fixed length means one hash function always gives the same output size.
That repeatability is what makes password checking work.
Password storage and login
- A user creates a password.
- The system hashes it.
- The system stores the hash, not the plaintext password.
At login:
- The user enters a password.
- The system hashes the entered password the same way.
- The system compares that new hash to the stored one.
- Matching hashes mean the password is accepted.
Salt
A salt is random data added to a password before hashing. Each user gets a unique salt.
- Two users with the same password will still have different stored hashes
- Salt makes rainbow tables much less useful
- The salt is stored too, because the system needs it again during login
Also know the weak hashes to avoid in secure settings. MD5 and SHA-1 are deprecated because attackers found efficient ways to force collisions.
Types of Password Attacks
There are two big categories.
Online and offline
| Type | Where guesses happen | Lockout helps | Visible to target system |
|---|---|---|---|
| Online | Live login portal | Yes | Yes |
| Offline | Attacker’s own computer using stolen hashes | No | No |
This distinction gets tested a lot. If hashes are stolen, account lockout does not stop offline cracking.
Main attack methods
- Leaked and reused credentials mean one breach can lead to access on another site because users reuse passwords.
- Password spraying tries one common password against many accounts, like
Fall2026!. - Credential stuffing uses stolen username-password pairs or default credentials, especially on routers, switches, and IoT devices.
- Brute force tests all possible passwords in a search space.
- Dictionary attack tests a list of likely passwords and patterns.
- Rainbow table attack searches a precomputed password-hash table for a match. Salts weaken this attack a lot.
Authentication Factors and MFA
There are four factor categories you need to know as a set:
- Something you know such as a password, PIN, or challenge question
- Something you have such as a phone, card, or token
- Something you are such as a fingerprint, face, iris, retina, or voice
- Somewhere you are such as GPS, Wi-Fi, time zone, or IP-based location
MFA means at least two different factor categories.
- Password + phone code = MFA
- Bank card + PIN = MFA
- Password + fingerprint = MFA
The exam trap is simple. Password + PIN is not MFA because both are knowledge factors.
Login Settings That Improve Security
These settings work best together, not alone:
- Password complexity requires character types such as uppercase, lowercase, numbers, and special characters.
- Minimum password length matters a lot because longer passwords sharply increase cracking difficulty.
- Maximum password age is often 90 to 120 days. It can limit use of a compromised password, but it can also cause predictable patterns like
PasswordFall2028. - Password history stores previous password hashes, often 5 to 10, to block reuse.
- Account lockout locks an account after about 3 to 5 failed attempts. This helps against online attacks only.
Key Takeaways
Authentication
The process of verifying that a user is who the user claims to be
Authentication Mechanism
A technical control that verifies a user's identity so only authorized users can access a system
Authentication Factor
Evidence a user supplies to prove identity, categorized as knowledge, possession, biometric, or location
Cryptographic Hash Function / Message Digest Function
A mathematical algorithm that converts binary data of arbitrary length into a fixed-length binary output
Hash / Hash Output / Checksum / Message Digest / Digest
The fixed-length binary string produced by a cryptographic hash function
Possible Outputs of an n-Bit Hash
An n-bit hash has 2^n possible outputs
Collision
The result when two different inputs produce the same hash output
Collision Resistance
The property that makes it computationally difficult to find two different inputs with the same hash
Pre-Image Resistance
The property that makes it computationally infeasible to determine an input that generated a given hash
Repeatability
The property that the same input processed by the same hash function always produces the same hash
Fixed Length
The property that a particular hash function always produces the same number of output bits regardless of input size
Deprecated Hash Function
A hash function no longer used in secure settings, usually because an efficient collision method exists; MD5 and SHA-1 are examples
Password Hashing and Verification
Store a password's hash instead of its plaintext, then hash each entered password and compare the result with the stored hash
Salt / Password Salting
A unique random value combined with a user's password before hashing so identical passwords produce different stored hashes
Online Password Attack
An attack that submits username-and-password guesses to an active login portal, service, or device
Offline Password Attack
An attack that tests candidate passwords against captured password hashes on the adversary's computer, bypassing account lockout
Password Spraying
Trying one common password or a few common passwords across many different user accounts
Credential Stuffing
Trying complete credentials stolen elsewhere or common default credentials against accounts, services, or devices
Brute-Force Attack
An automated offline attack that systematically tests every potential password in a chosen search space
Dictionary Attack
An automated offline attack that tests a list of common or likely passwords instead of every possible string
Rainbow Table
A precomputed table associating potential passwords with their hash outputs, sorted by hash for searching
Rainbow Table Attack
Searching a precomputed rainbow table for a captured hash to identify an associated password
Knowledge Factor
Something the user knows, such as a password, PIN, or challenge-question answer
Possession Factor
An object the user has, such as an access card, bank card, registered phone, or authentication token
Biometric Factor
A measured bodily feature, such as a fingerprint, face, iris, retina, palm print, or voice
Location Factor
Evidence of somewhere the user is, inferred from data such as Wi-Fi signals, GPS, time zone, or IP address
Multifactor Authentication (MFA)
Authentication requiring at least two different factor categories, not merely two pieces of the same type of evidence
Password Complexity Requirement
A login rule requiring characters from designated sets, commonly uppercase, lowercase, numeric, and special characters
Minimum Password Length
A login rule requiring a password to contain at least a configured number of characters
Maximum Password Age
The maximum time a password may remain in use before a change is required, though routine changes can encourage predictable patterns
Password History
A stored set of previous password hashes used to reject recently reused passwords
Account Lockout
A setting that locks an account after a configured number of invalid login attempts, limiting online but not offline guessing
Notes
Authentication
The process of verifying that a user is who the user claims to be
Authentication Mechanism
A technical control that verifies a user's identity so only authorized users can access a system
Authentication Factor
Evidence a user supplies to prove identity, categorized as knowledge, possession, biometric, or location
Cryptographic Hash Function / Message Digest Function
A mathematical algorithm that converts binary data of arbitrary length into a fixed-length binary output
Hash / Hash Output / Checksum / Message Digest / Digest
The fixed-length binary string produced by a cryptographic hash function
Possible Outputs of an n-Bit Hash
An n-bit hash has 2^n possible outputs
Collision
The result when two different inputs produce the same hash output
Collision Resistance
The property that makes it computationally difficult to find two different inputs with the same hash
Pre-Image Resistance
The property that makes it computationally infeasible to determine an input that generated a given hash
Repeatability
The property that the same input processed by the same hash function always produces the same hash
Fixed Length
The property that a particular hash function always produces the same number of output bits regardless of input size
Deprecated Hash Function
A hash function no longer used in secure settings, usually because an efficient collision method exists; MD5 and SHA-1 are examples
Password Hashing and Verification
Store a password's hash instead of its plaintext, then hash each entered password and compare the result with the stored hash
Salt / Password Salting
A unique random value combined with a user's password before hashing so identical passwords produce different stored hashes
Online Password Attack
An attack that submits username-and-password guesses to an active login portal, service, or device
Offline Password Attack
An attack that tests candidate passwords against captured password hashes on the adversary's computer, bypassing account lockout
Password Spraying
Trying one common password or a few common passwords across many different user accounts
Credential Stuffing
Trying complete credentials stolen elsewhere or common default credentials against accounts, services, or devices
Brute-Force Attack
An automated offline attack that systematically tests every potential password in a chosen search space
Dictionary Attack
An automated offline attack that tests a list of common or likely passwords instead of every possible string
Rainbow Table
A precomputed table associating potential passwords with their hash outputs, sorted by hash for searching
Rainbow Table Attack
Searching a precomputed rainbow table for a captured hash to identify an associated password
Knowledge Factor
Something the user knows, such as a password, PIN, or challenge-question answer
Possession Factor
An object the user has, such as an access card, bank card, registered phone, or authentication token
Biometric Factor
A measured bodily feature, such as a fingerprint, face, iris, retina, palm print, or voice
Location Factor
Evidence of somewhere the user is, inferred from data such as Wi-Fi signals, GPS, time zone, or IP address
Multifactor Authentication (MFA)
Authentication requiring at least two different factor categories, not merely two pieces of the same type of evidence
Password Complexity Requirement
A login rule requiring characters from designated sets, commonly uppercase, lowercase, numeric, and special characters
Minimum Password Length
A login rule requiring a password to contain at least a configured number of characters
Maximum Password Age
The maximum time a password may remain in use before a change is required, though routine changes can encourage predictable patterns
Password History
A stored set of previous password hashes used to reject recently reused passwords
Account Lockout
A setting that locks an account after a configured number of invalid login attempts, limiting online but not offline guessing
