Topic 3.4 Notes – Protecting Networks: Firewalls
What Firewalls Are and What They Control
A firewall is a security control that allows or denies network traffic crossing a boundary. That boundary might be the edge of the whole network or just one segment inside it. The firewall itself is usually software, even if it lives on a dedicated firewall box, a router, or another security device.
Its job is to create a controlled boundary between areas with different trust levels.
- Inbound traffic is entering the protected segment.
- Outbound traffic is leaving that segment.
- Direction is always relative to the segment or interface you’re protecting.
A firewall can make decisions using:
- Source and destination IP addresses
- Source and destination logical ports
- Port 22 = SSH
- Port 80 = HTTP
- Protocol such as TCP, UDP, or ICMP
- Service or application
- Connection state if the firewall is stateful
A logical port is a network service endpoint, not a physical switch port. That shows up on tests a lot.
A firewall only controls traffic that passes through it. In a segmented network, that can mean one firewall at the edge and others protecting internal systems or guest access.
- Rogue access point bypasses the firewall → firewall cannot stop that path
- Allowed traffic can still be malicious → “allowed” only means it matched the rule
Types of Network-Based Firewalls
These three types mainly differ in how much context they use.
Stateless firewalls
A stateless firewall checks each packet by itself. It uses header info like IP addresses, ports, and protocol.
- It does packet-by-packet filtering
- It does not remember earlier packets
- It does not know whether a connection was already established
Stateful firewalls
A stateful firewall does header filtering too, but it also tracks whether traffic belongs to an existing connection. This is why you’ll also hear dynamic packet filtering.
Example:
- Internal device makes an allowed outbound TCP connection
- Return packets come back
- Stateful firewall recognizes them as part of that connection
- Random inbound packets that are not part of it can still be blocked
That “return traffic from an allowed connection” idea is the most important difference from stateless filtering.
Next-generation firewalls
A next-generation firewall includes stateless and stateful features, plus more advanced inspection.
Common added features:
- Intrusion prevention
- Deep packet inspection
- Application filtering
This matters because traffic does not always stay on the “expected” port, and many apps share ports like 80 and 443.
How ACLs Make Firewall Decisions
An ACL or access control list is the ordered rule set the firewall follows. The firewall enforces. The ACL tells it what to do.
A typical rule includes:
- Direction such as inbound or outbound
- Match criteria such as IP, port, protocol, service, or application
- Action such as allow/permit or deny
Rule order
ACLs are checked top to bottom. The first matching rule wins.
That means a later rule does nothing if traffic already matched an earlier one.
| Rule | Direction | Protocol | Source | Destination Port | Action |
|---|---|---|---|---|---|
| 1 | Inbound | TCP | 203.0.113.0/24 | 22 | ALLOW |
| 2 | Inbound | TCP | ALL | ALL | DENY |
This allows SSH only from the admin subnet, then blocks the rest of inbound TCP. The example below shows that same first-match logic in a firewall ACL.
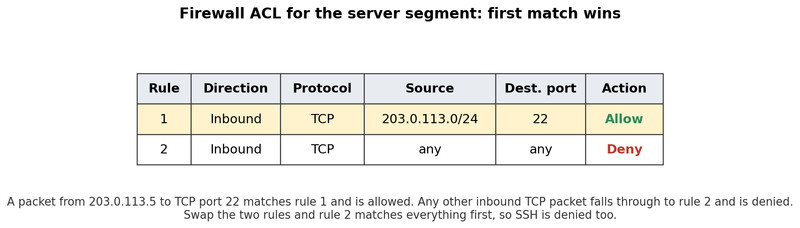
ACL first-match rule order
Shadowing
Shadowing happens when a broad rule appears before a specific one.
DENY inbound TCP ALL from ALLALLOW inbound TCP destination port 22 from 203.0.113.0/24
Here, the deny rule matches first, so the SSH allow rule never applies.
Writing Firewall Rules from Requirements
A requirement has to become a precise rule. You’re translating words into filters.
- Identify the boundary
- Decide inbound or outbound
- Identify the source
- Identify the destination if needed
- Choose the protocol
- Choose the port, service, or application
- Choose allow or deny
- Put the rule in the right order
Example requirement: only admin subnet 203.0.113.0/24 can use SSH to manage a server.
ALLOW inbound TCP destination port 22 from 203.0.113.0/24DENY inbound TCP ALL from ALL
On FRQs, “allow SSH” is too vague. You usually need direction, protocol, port, and source at minimum.
Where Firewalls Should Be Placed
Placement decides what traffic the firewall can even see.
- Every internet ingress and egress point should have a firewall
- Each network segment should have firewall control over traffic entering and leaving it
- Different segments can have different rule sets
A common layout looks like this, with a public-facing zone separated from the internal network:
- Perimeter firewall at the internet edge
- DMZ for public-facing servers
- Another firewall boundary between DMZ and internal network
- Internal segmentation for employees, admins, sensitive servers, and guests
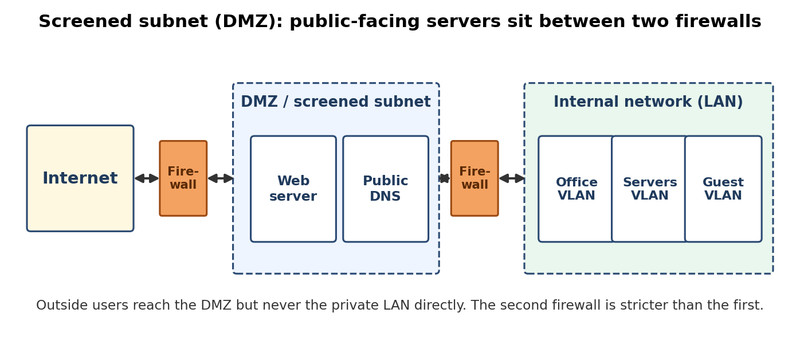
Firewall placement with a DMZ
This supports defense in depth and limits lateral movement after a compromise.
Key Takeaways
Firewall
Software that applies configured rules to permit or deny network traffic crossing a network or segment boundary
Stateless Firewall
A firewall that evaluates each packet independently using header information such as IP addresses, ports, and protocol, without tracking connections
Stateful Firewall / Dynamic Packet-Filtering Firewall
A firewall that filters packet headers and tracks connection state, allowing it to distinguish expected connection traffic from unrelated traffic
Next-Generation Firewall (NGFW)
A firewall combining stateless and stateful filtering with advanced features such as deep packet inspection, intrusion prevention, and application filtering
Logical Port
A numbered TCP or UDP network endpoint associated with a service, such as TCP port 22 for SSH; it is not a physical switch port
Inbound vs. Outbound Traffic
Inbound traffic enters the segment or zone named by a rule; outbound traffic leaves it, so direction is relative to the protected boundary
Access Control List (ACL)
An ordered set of firewall rules specifying which inbound or outbound traffic to permit or deny based on criteria such as addresses, ports, protocols, services, or applications
First-Match Rule
ACL rules are evaluated from top to bottom, and the first matching rule is executed while all later rules are ignored for that traffic
Default-Deny Approach
Permit only specifically required traffic, place those narrow exceptions first, and use a broader later rule to deny the remaining traffic
Translating Firewall Requirements into ACL Rules
Identify the boundary, direction, source, destination, protocol, port, service or application, allow-or-deny action, and position relative to broader or overlapping rules
Firewall Placement
Place firewall controls at every internet ingress and egress point and at each network-segment boundary, using policies appropriate to each segment
Notes
Firewall
Software that applies configured rules to permit or deny network traffic crossing a network or segment boundary
Stateless Firewall
A firewall that evaluates each packet independently using header information such as IP addresses, ports, and protocol, without tracking connections
Stateful Firewall / Dynamic Packet-Filtering Firewall
A firewall that filters packet headers and tracks connection state, allowing it to distinguish expected connection traffic from unrelated traffic
Next-Generation Firewall (NGFW)
A firewall combining stateless and stateful filtering with advanced features such as deep packet inspection, intrusion prevention, and application filtering
Logical Port
A numbered TCP or UDP network endpoint associated with a service, such as TCP port 22 for SSH; it is not a physical switch port
Inbound vs. Outbound Traffic
Inbound traffic enters the segment or zone named by a rule; outbound traffic leaves it, so direction is relative to the protected boundary
Access Control List (ACL)
An ordered set of firewall rules specifying which inbound or outbound traffic to permit or deny based on criteria such as addresses, ports, protocols, services, or applications
First-Match Rule
ACL rules are evaluated from top to bottom, and the first matching rule is executed while all later rules are ignored for that traffic
Default-Deny Approach
Permit only specifically required traffic, place those narrow exceptions first, and use a broader later rule to deny the remaining traffic
Translating Firewall Requirements into ACL Rules
Identify the boundary, direction, source, destination, protocol, port, service or application, allow-or-deny action, and position relative to broader or overlapping rules
Firewall Placement
Place firewall controls at every internet ingress and egress point and at each network-segment boundary, using policies appropriate to each segment
