Topic 5.3 Notes – Protecting Stored Data with Cryptography
Protecting Stored Data with Encryption
When a file is sitting on a laptop, USB drive, or disk, anyone who gets access to that storage might be able to read it. Encryption changes the file into unreadable ciphertext unless someone also has the right key.
- Cryptography hides information.
- Encryption turns plaintext into ciphertext.
- Decryption turns ciphertext back into plaintext with the correct key.
- Algorithm means the procedure.
- Key means the secret value that controls the transformation.
The core relationship is:
- plaintext + key + encryption algorithm → ciphertext
- ciphertext + correct key + decryption algorithm → plaintext
The file example below puts that relationship into a concrete form.
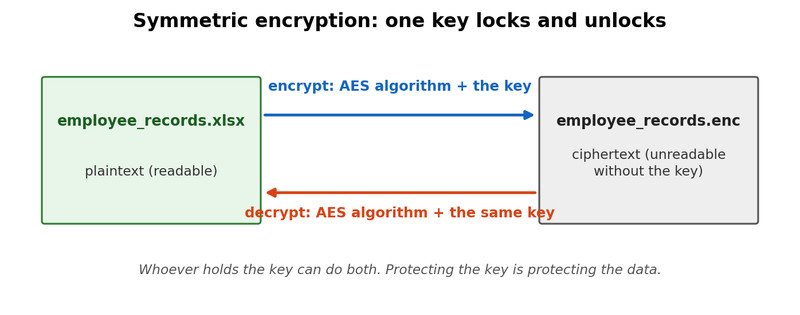
File encryption and decryption
Plaintext can be any unencrypted file, not just words on a page. It could be a spreadsheet, image, database, video, or executable.
This protects confidentiality. If someone steals an encrypted external drive, they can copy the file, but they cannot read it without the key. That matters because encryption is one layer in defense in depth along with physical security and access controls.
Encryption has limits. It does not stop someone from deleting the file, locking you out of it, or reading it if they steal both the file and the key. It also protects the file most directly while it is stored, because data usually has to be decrypted before use.
The Main Cryptography Classifications
Symmetric and asymmetric encryption
Symmetric encryption uses the same key to encrypt and decrypt. That is the main type used for file encryption in this topic.
Asymmetric encryption uses two different but related keys. You only need the basic distinction here. The detailed public/private key use belongs in the next topic.
Block and stream encryption
Block ciphers process data in fixed-size chunks called blocks.
Stream ciphers process data continuously, commonly described here as one bit at a time.
One easy trap is mixing up block size and key length. They are different things.
Keyspace and brute force
Keyspace is the total number of possible keys an algorithm can use. A larger keyspace means a brute-force attacker has more possibilities to guess through.
Still, security is never just “longer key = solved.”
- The algorithm must be strong.
- The key must be generated and stored securely.
- Users must not expose the key.
- A password may be used to derive the key instead of being the raw key itself.
That last point shows up in OpenSSL. The -k option gives a password, and the software derives the AES key from it.
AES as the File Encryption Example
AES stands for Advanced Encryption Standard. It is the most common symmetric encryption algorithm and the one you should think of first for this topic.
- AES is a symmetric-key block cipher
- It always uses 128-bit blocks, which is 16 bytes
- It supports 128-bit, 192-bit, and 256-bit keys
This diagram is useful for keeping the block size and key size separate in your head.
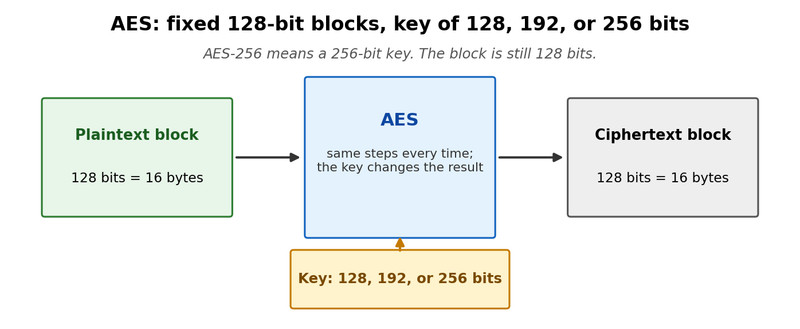
AES block size versus key size
The most tested misunderstanding here is this:
- AES-256 means a 256-bit key
- It does not mean 256-bit blocks
In the figure, the plaintext and ciphertext are both 16 bytes, and only the key length changes between AES versions.
Longer AES keys create a larger keyspace, so brute-force guessing becomes harder. They also take more time to encrypt and decrypt.
You’ll see AES used in:
- Wi-Fi security
- protections used in internet browsing
- file encryption
- full-disk encryption
- hardware-level processor encryption
Encrypting and Decrypting Files with OpenSSL
Files can be encrypted with the command line, with specialized software such as AES Crypt, or with web-based tools. OpenSSL is the command-line method you’re most likely to be tested on.
Encrypting a file
openssl enc -aes-128-cbc -e -in test -k password -out test.enc
What each part means:
encchooses symmetric encryption functions-aes-128-cbcchooses AES with a 128-bit key-emeans encrypt-in testis the plaintext input file-k passwordgives the password used to derive the key-out test.encwrites the ciphertext output
Decrypting a file
openssl enc -aes-128-cbc -d -in test.enc -k password -out test
-dmeans decrypt- you must use the same password-derived key
- changing the password or algorithm prevents recovery of the original file
A common exam trap is forgetting that encrypting creates an encrypted copy, but the original plaintext file may still exist.
What Encryption Protects and What It Does Not
Encryption protects stored files when an attacker gets the ciphertext but not the key. That protection depends on a good algorithm like AES, a strong enough key length, and safe handling of the key and any plaintext copies.
It does not guarantee integrity, prevent deletion, or keep data secret if the key is exposed with the file.
Key Takeaways
Stored Data (Data at Rest)
Data saved on a drive or other storage medium rather than actively being transmitted or processed
Cryptography
The use of algorithms and keys to hide information and allow it to be recovered with the correct key
Cryptographic Algorithm
A defined process for encrypting and decrypting information
Encryption
The process of hiding information by transforming plaintext into ciphertext
Decryption
The process of reversing encryption with the correct key to recover the original plaintext
Plaintext
The original unencrypted binary data supplied to an encryption algorithm
Ciphertext
The encrypted output of an encryption algorithm, ordinarily meaningless without the appropriate key
Cryptographic Key
A predefined value that controls the particular transformation performed during encryption or decryption
Keyspace
The number of possible keys an algorithm can use; a larger keyspace makes discovering the correct key by guessing take longer
Symmetric Encryption (Symmetric-Key Encryption)
Encryption that uses the same shared secret key to encrypt and decrypt information
Asymmetric Encryption
Encryption that uses two different related keys, one to encrypt information and the other to decrypt it
Block Cipher (Block Encryption)
Encryption that processes data in fixed-size chunks called blocks, producing an output block for each input block
Stream Cipher (Stream Encryption)
Encryption that handles input continuously and produces output one element, commonly one bit, at a time
Advanced Encryption Standard (AES)
The most common symmetric-key block cipher; it processes 128-bit blocks using 128-, 192-, or 256-bit keys
OpenSSL AES-128-CBC File Encryption Command
Openssl enc -aes-128-cbc -e -in test -k password -out test.enc
OpenSSL AES-128-CBC File Decryption Command
Openssl enc -aes-128-cbc -d -in test.enc -k password -out test
Notes
Stored Data (Data at Rest)
Data saved on a drive or other storage medium rather than actively being transmitted or processed
Cryptography
The use of algorithms and keys to hide information and allow it to be recovered with the correct key
Cryptographic Algorithm
A defined process for encrypting and decrypting information
Encryption
The process of hiding information by transforming plaintext into ciphertext
Decryption
The process of reversing encryption with the correct key to recover the original plaintext
Plaintext
The original unencrypted binary data supplied to an encryption algorithm
Ciphertext
The encrypted output of an encryption algorithm, ordinarily meaningless without the appropriate key
Cryptographic Key
A predefined value that controls the particular transformation performed during encryption or decryption
Keyspace
The number of possible keys an algorithm can use; a larger keyspace makes discovering the correct key by guessing take longer
Symmetric Encryption (Symmetric-Key Encryption)
Encryption that uses the same shared secret key to encrypt and decrypt information
Asymmetric Encryption
Encryption that uses two different related keys, one to encrypt information and the other to decrypt it
Block Cipher (Block Encryption)
Encryption that processes data in fixed-size chunks called blocks, producing an output block for each input block
Stream Cipher (Stream Encryption)
Encryption that handles input continuously and produces output one element, commonly one bit, at a time
Advanced Encryption Standard (AES)
The most common symmetric-key block cipher; it processes 128-bit blocks using 128-, 192-, or 256-bit keys
OpenSSL AES-128-CBC File Encryption Command
Openssl enc -aes-128-cbc -e -in test -k password -out test.enc
OpenSSL AES-128-CBC File Decryption Command
Openssl enc -aes-128-cbc -d -in test.enc -k password -out test
